DPDP Compliance for Banking, Financial Services & Insurance
Protect Financial Data. Strengthen Privacy. Build a Structured DPDP Compliance Framework.
Compliance Scope & Regulatory Focus
Banks, financial institutions, NBFCs, fintech companies and insurance organizations process large volumes of personal and financial information across customer onboarding, transactions, lending, insurance, digital platforms and third-party systems.
RARR Technologies helps BFSI organizations establish a structured approach to data discovery, gap analysis, data classification, privacy, security, data retention, breach response and third-party risk management.
Data Areas We Can Help Address
Our DPDP Compliance & Data Protection Services
A comprehensive six-phase methodology to achieve complete regulatory alignment and mitigate operational risks.
Gap Analysis
Identify Compliance Gaps. Strengthen Your Data Protection Framework.
Assess existing privacy, security, governance and operational practices to identify gaps and develop a structured remediation roadmap.
Data Discovery
Discover, Map & Understand Your Financial Data.
Identify personal data across banking applications, CRM, core systems, lending platforms, insurance systems, websites, mobile applications and databases.
Data Classification
Classify Data. Protect What Matters.
Categorize personal data based on its type, purpose, sensitivity and processing requirements to support appropriate security, access and retention controls.
Data Leakage Prevention
Prevent Unauthorized Data Exposure.
Identify potential risks related to unauthorized access, sharing or exposure of customer and employee information across applications, systems and endpoints.
IT & Operations
Strengthen IT Security & Privacy Operations.
Review access management, security controls, monitoring, logging, vulnerability management and incident-response practices to support a structured data protection environment.
TPRM / Third-Party Risk Management
Manage Third-Party Data & Privacy Risks.
Assess banks’ and financial organizations’ technology providers, processors, fintech partners, insurance partners and other third parties that handle personal data.
Comprehensive Privacy & Governance Framework
End-to-end mechanisms for consent, rights fulfillment, retention policies, and security operations.
Privacy Notice & Consent Management
Build Transparent Customer Data Practices.
Establish structured privacy notices and consent processes where applicable, covering the purpose of processing, categories of personal data, applicable rights and mechanisms for consent withdrawal.
Data Retention & Deletion
Retain Data Responsibly. Delete When No Longer Required.
Develop documented retention and deletion processes across customer, employee, marketing, service and third-party data environments.
Data Principal Rights
Create a Structured Process for Data Rights Requests.
Establish processes for handling applicable data principal requests and consent withdrawal in a consistent and documented manner.
Security & Access Controls
Strengthen Protection Across Your Data Ecosystem.
Support appropriate technical and organizational measures across core and digital banking environments:
- Role-based access controls (RBAC)
- Data encryption in transit and at rest
- Network segmentation & firewall rules
- Regular vulnerability assessments & penetration testing
- Centralized audit logging & continuous monitoring
- Incident response & breach escalation plans
Data Breach Response
Detect. Assess. Notify. Remediate.
Establish a structured process for detecting, assessing and responding to personal data breaches, including appropriate statutory notifications and remediation activities.
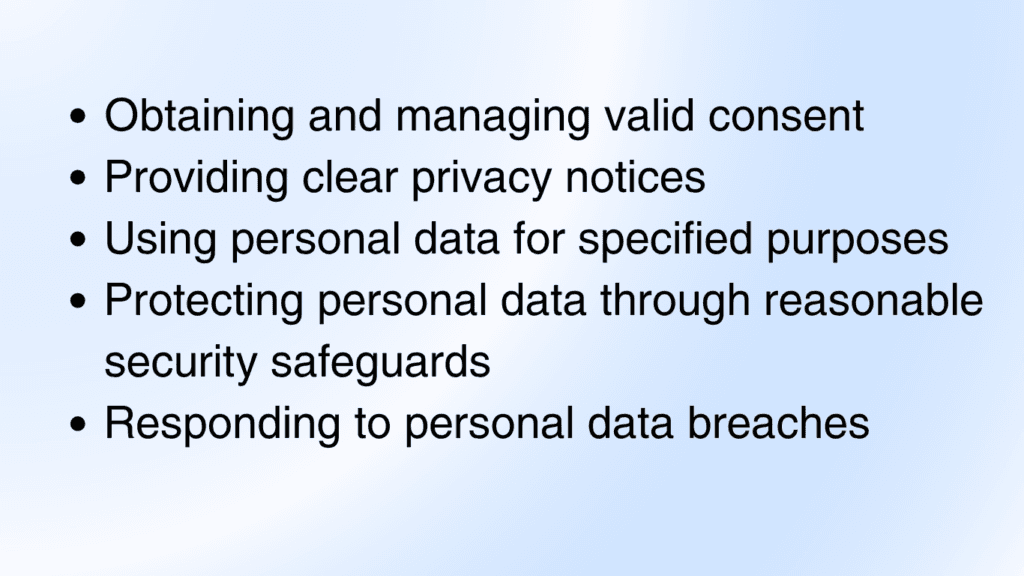
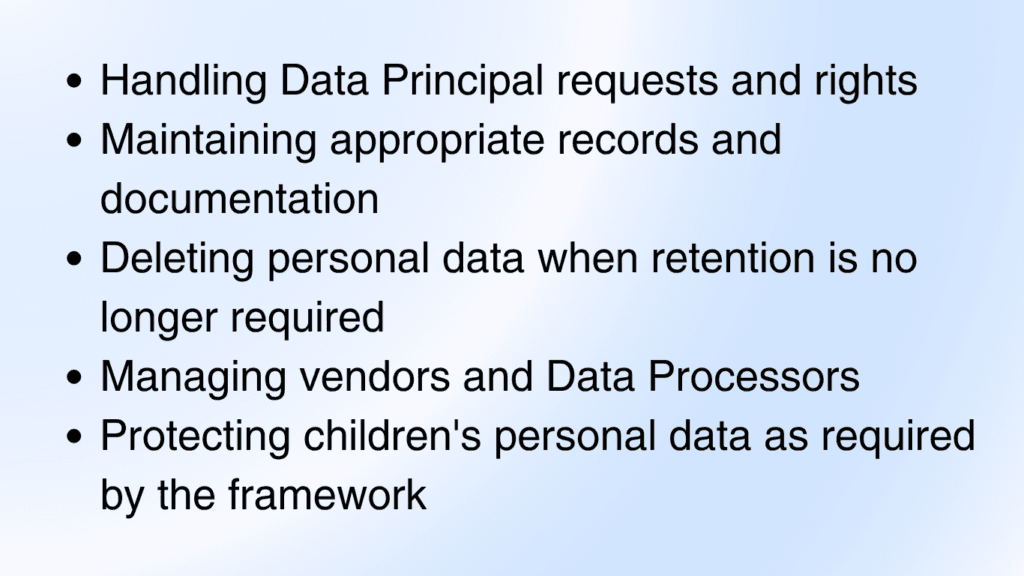
Key Deliverables & Safeguards
Structured documentation, consent workflows, security architectures, and compliance artifacts.
Why RARR Technologies?
Technology + Compliance Approach
RARR Technologies helps BFSI organizations build a structured approach to data visibility, privacy, security, governance and third-party risk management. From data discovery and gap analysis to IT operations and TPRM, we help organizations establish processes designed around their data environment and compliance requirements.
Protect Financial Data. Strengthen Privacy. Build Trust.
Talk to Our DPDP Experts
Protect customer data, maintain continuous audit readiness, and prevent statutory penalties.
Get Free Consultation